Generic / Other
Use this preset for any SAML 2.0 IdP without a dedicated tab — Ping Identity, ADFS, OneLogin, Shibboleth, or something in-house.
The protocol is identical. Only the vocabulary changes, so this preset shows the standard SAML names and leaves the attribute mapping fully editable.
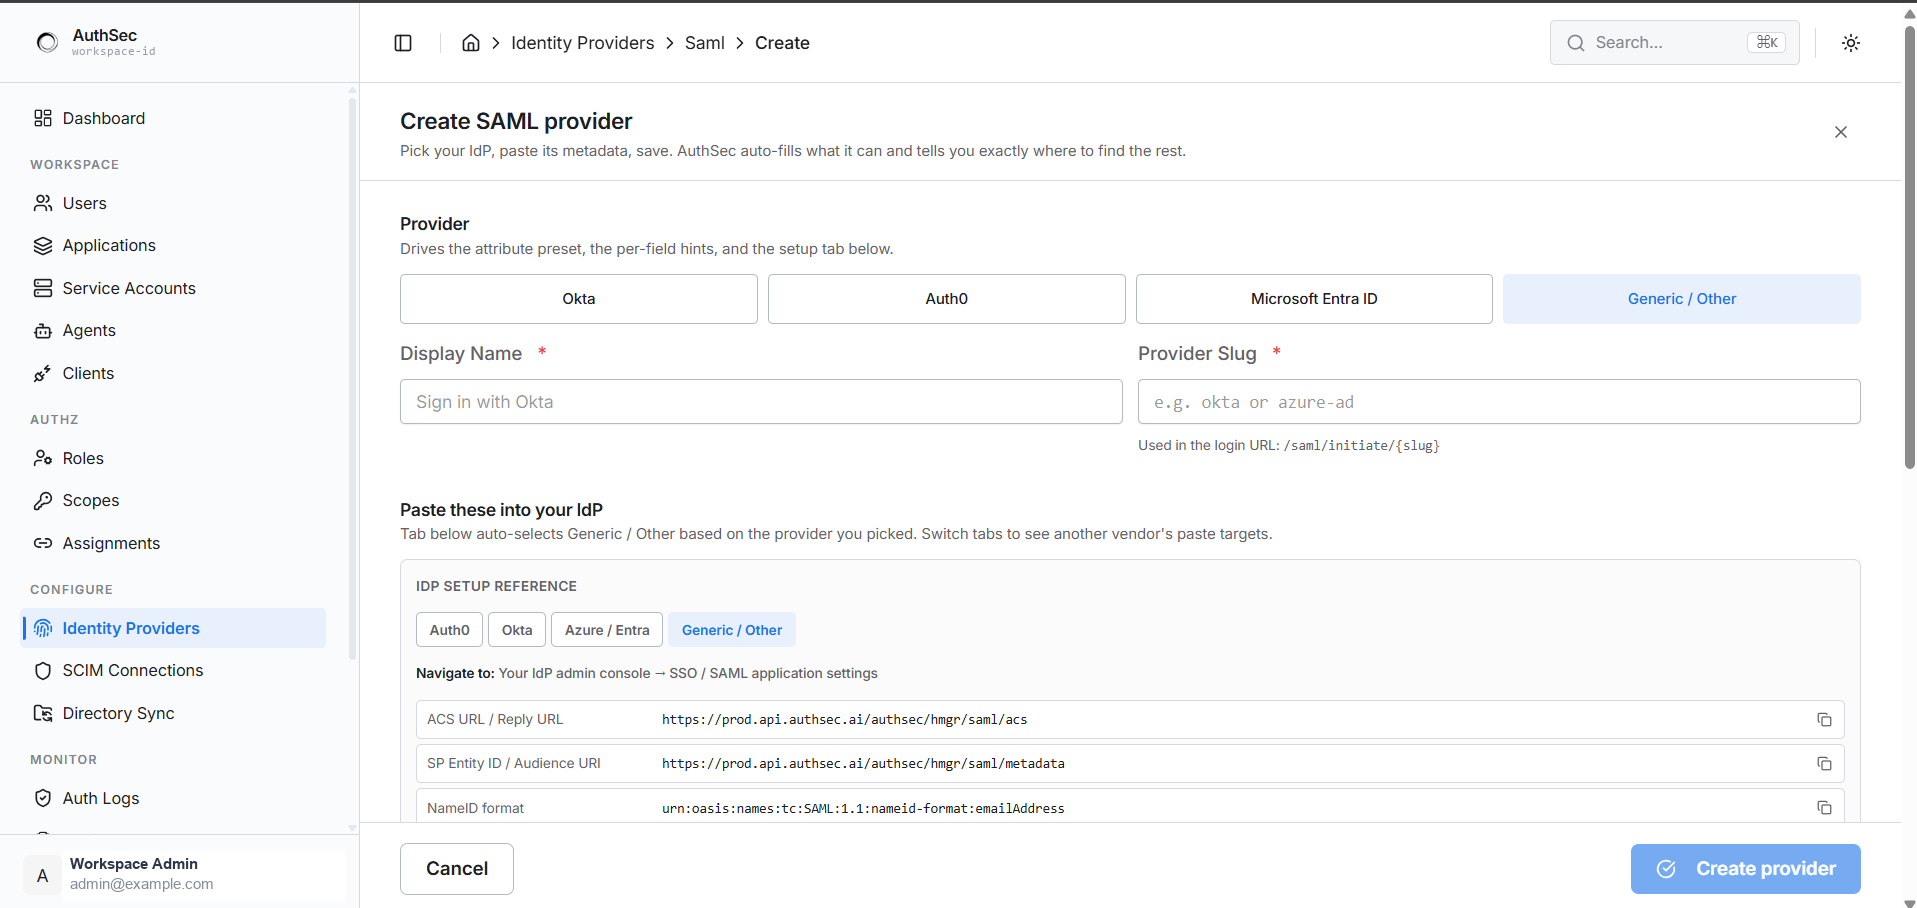
1. In AuthSec
Identity Providers → + Add provider → SAML 2.0, then pick Generic / Other.
2. In your IdP
Create a SAML 2.0 application — usually under an admin console's SSO or SAML section — and register these:
| AuthSec provides | Standard SAML name | Also called |
|---|---|---|
| ACS URL / Reply URL | AssertionConsumerServiceURL | Single sign-on URL, Callback URL, Destination |
| SP Entity ID / Audience URI | SP EntityID | Audience, Identifier, Relying Party ID |
| NameID format | urn:oasis:names:tc:SAML:1.1:nameid-format:emailAddress | Unique identifier |
3. Back in AuthSec
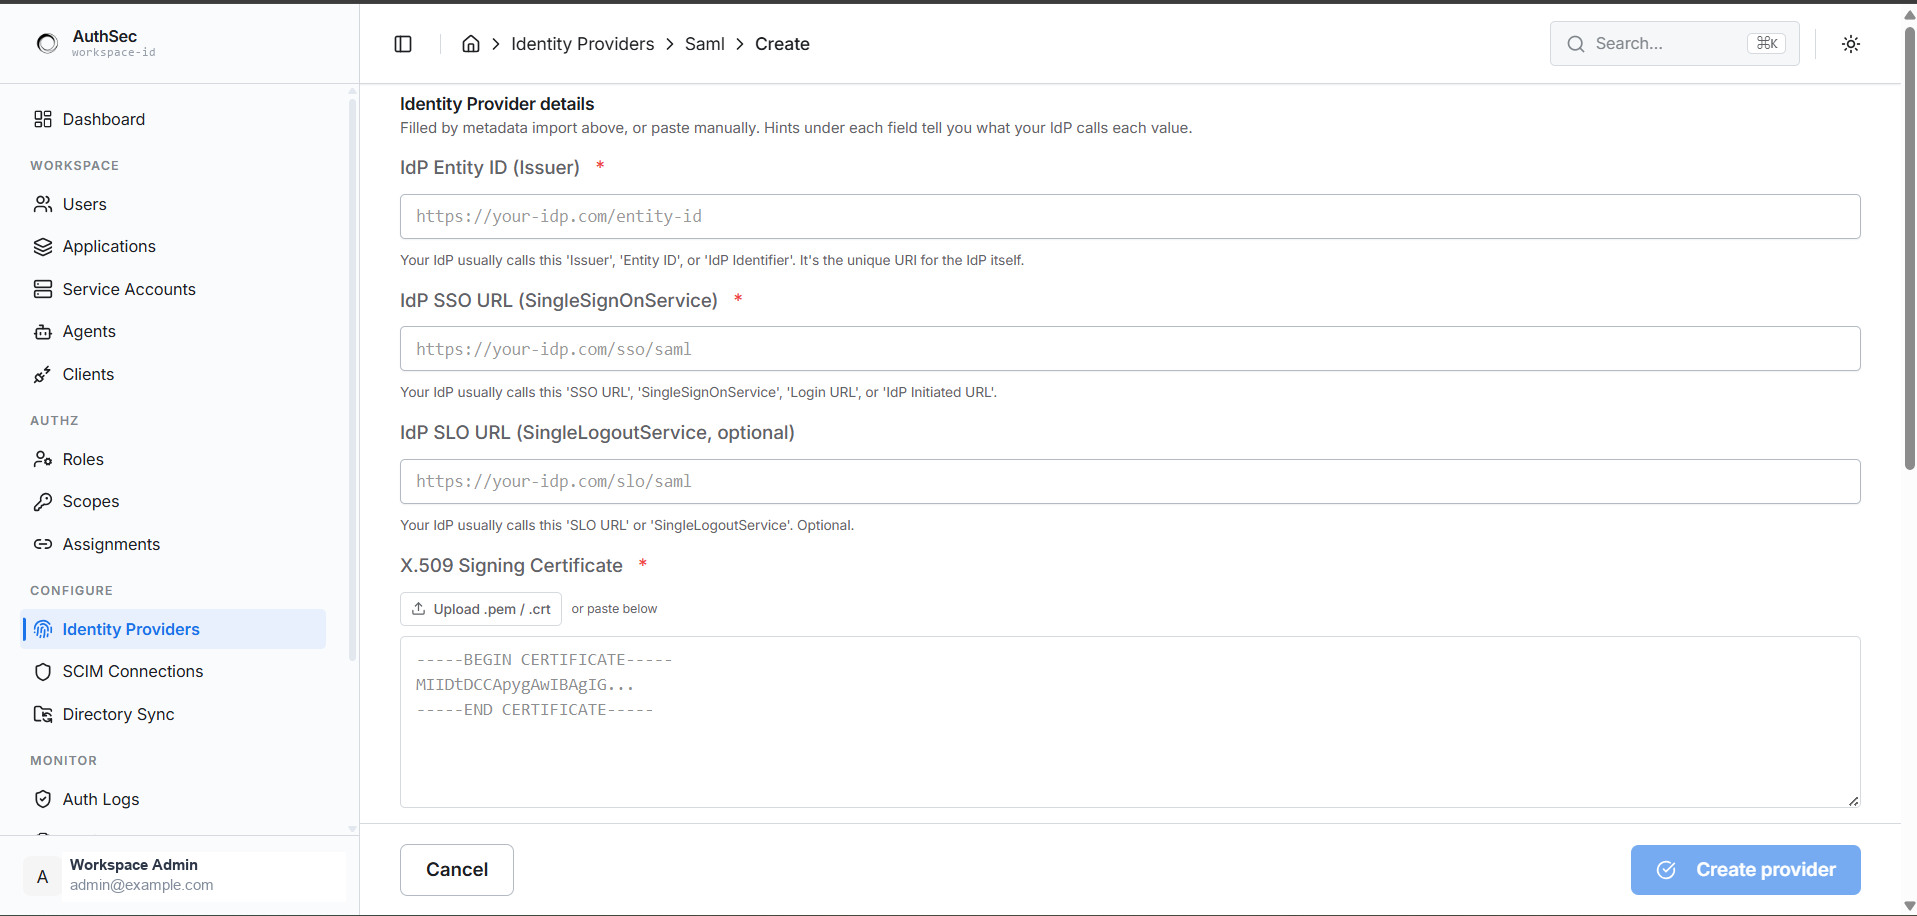
Most IdPs publish a metadata document — look for "Federation Metadata", "SAML 2.0 Metadata", or an /idp/metadata URL. Paste it into Import IdP metadata XML and click Apply metadata.
Filling in manually, here is the same value under different vendors' names:
| AuthSec field | What your IdP may call it |
|---|---|
| IdP Entity ID (Issuer) | Issuer, EntityID, IdP Identifier |
| IdP SSO URL | SSO URL, SingleSignOnService, Login URL, IdP Initiated URL |
| IdP SLO URL | SLO URL, SingleLogoutService, Logout URL |
| X.509 Signing Certificate | Signing Certificate, Public Certificate, Token-signing certificate |
4. Attributes
There is no safe default here — check what your IdP actually emits and mirror it exactly.
| Style | Looks like |
|---|---|
| Short names | email, firstName, lastName |
| Schema URIs | http://schemas.xmlsoap.org/ws/2005/05/identity/claims/emailaddress |
| LDAP-ish | mail, givenName, sn |
ADFS and most Windows-lineage IdPs use schema URIs. Ping and OneLogin usually use short names.
Click Create provider.
Gotchas
- Read the IdP's own assertion. If sign-in works but fields are empty, the attribute names differ — the IdP's test or preview tool will show the exact names emitted.
- Certificate must be PEM with markers. A DER/binary
.cerwill not paste. Convert it, or export as Base64. - Clock skew breaks assertions. SAML assertions are time-bound; a server minutes out of sync fails validation with a misleading signature error.
- Some IdPs need the SP metadata as a file. AuthSec exposes the values individually — if your IdP insists on an upload, build the SP metadata XML around those values.